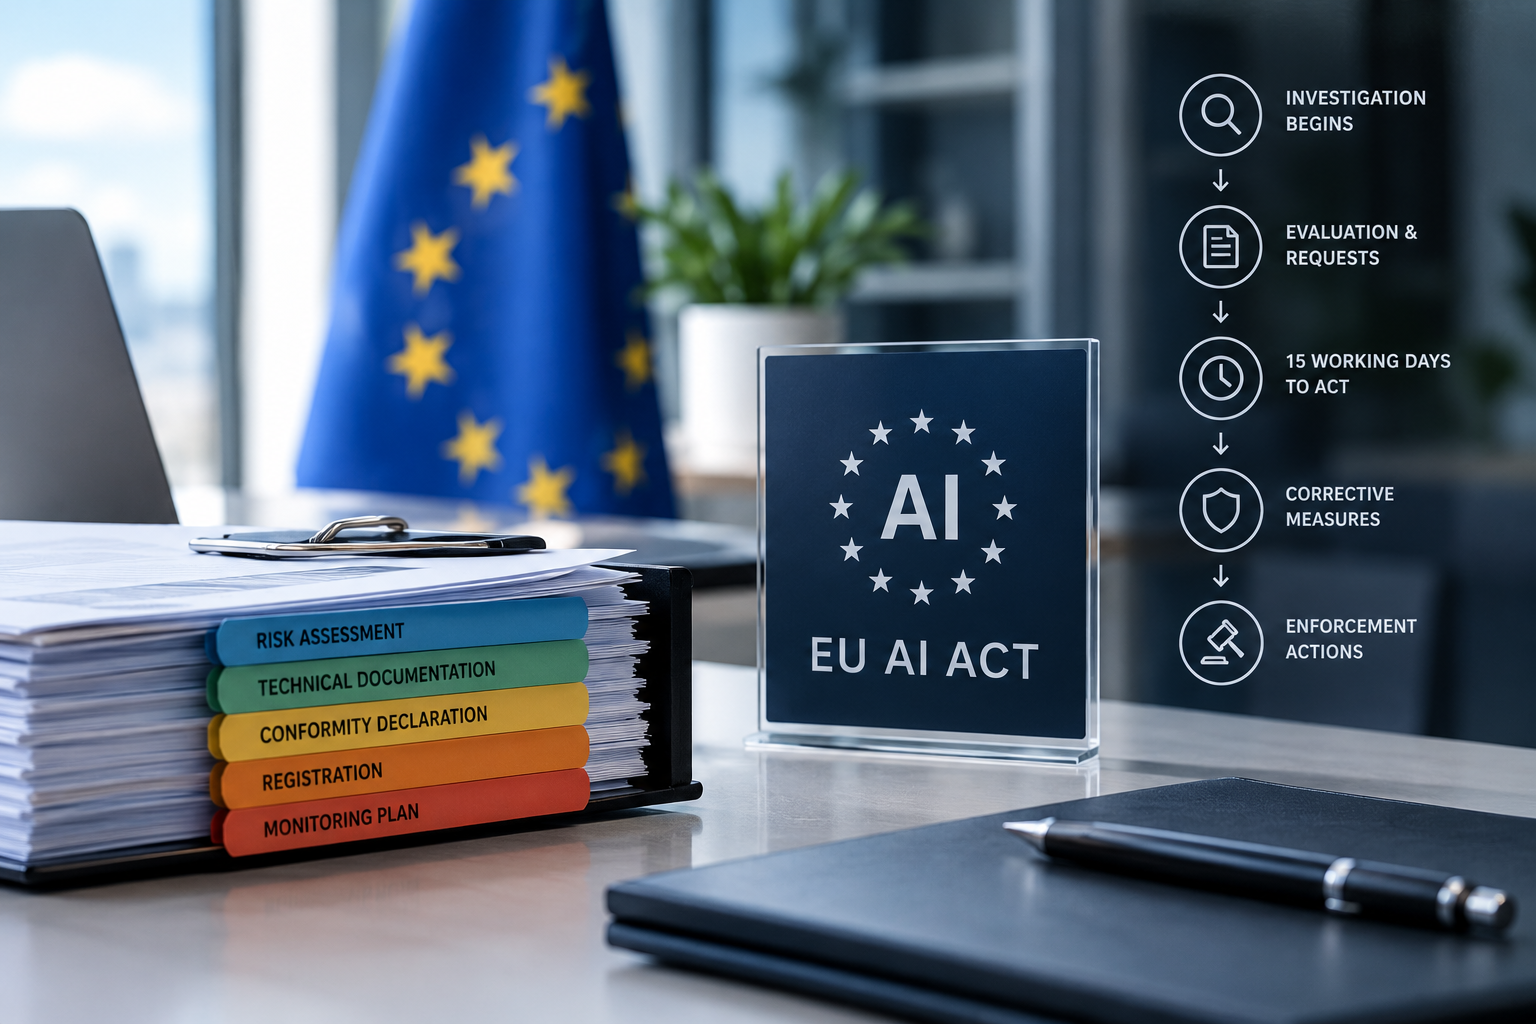
A market surveillance authority opens an investigation into your AI system. Here is exactly what happens next — step by step, with the deadlines attached.
Compliance conversations fixate on the fines. But the fine is the last thing that happens. Before any penalty, there is a process — a structured, legally defined procedure with defined powers and defined deadlines, up to and including the forced withdrawal of a system from the EU market. That procedure stopped being theoretical on 2 August 2026, when national authorities acquired their full powers. Understanding it is the difference between responding to an investigation from a documented position and building the documentation in real time while a regulator waits.
Who enforces
Two layers. National market surveillance authorities — designated by each Member State, with designations required by August 2025 and full powers held since 2 August 2026 — supervise AI systems, from the Article 5 prohibitions to the high-risk obligation set, wielding the established toolkit of Regulation (EU) 2019/1020 plus the Act’s own powers. Member States have routed the role differently — several to their data protection authorities, others to market or network regulators — and national activation has been staggered, which changes who knocks, not what they can do. The second layer is the European AI Office, with exclusive jurisdiction over general-purpose AI models and its own enforcement powers — and, where the same company provides both the model and a system built on it, the AI Office acts as market surveillance authority for that system too.
How an investigation begins
Three routes. A complaint under Article 85 — open to any natural or legal person with grounds to consider an infringement has occurred, competitors and journalists included, and the authority is obliged to handle it: a statutory pathway, not a discretionary one. Own-initiative monitoring — authorities can review systems in their market proactively, including remotely, without waiting for anyone. And cross-border escalation — where non-compliance is assessed as extending beyond one territory, the authority notifies the Commission and every other Member State, and a single national complaint can become a coordinated EU-wide action.
The evaluation — and what they can demand
The authority assesses the system against its applicable requirements — for high-risk systems, the full Chapter III, Section 2 set. Its powers while doing so are substantial: full access to documentation, including risk assessments, quality-management records and the training, validation and testing datasets; unannounced on-site inspections under the market surveillance framework; access to source code under specified conditions; and remote review of system behaviour. Operators hold the right to be heard before measures are taken — a due-process right, not a negotiation. Practitioners widely expect the investigative style to resemble EU competition proceedings: document-intensive, with drafts and internal communications read as evidence of what the organisation knew and intended. Companies without structured records will be reconstructing them under investigatory pressure — which is itself visible to the investigator.
The clock — fifteen working days
Where the evaluation finds non-compliance, Article 79 requires the authority to act without undue delay: the operator must be required to take all appropriate corrective action, withdraw the system, or recall it — within a period the authority may prescribe, and in any event within fifteen working days at most. Roughly three calendar weeks, ceiling not courtesy — and where the non-compliance crosses borders, the Commission and all Member States are notified in the same window. If adequate correction doesn’t follow, provisional measures land: prohibition, restriction, withdrawal or recall on the national market — operational interventions, not fines — with the details circulated EU-wide. Then Article 79(8)’s window runs: if no objection is raised within three months — thirty days where a prohibited practice is involved — the measures are deemed justified, and equivalent restriction follows across the Union.
The most likely first wave: paperwork, not deep audits
Article 83 lists the formal non-compliance findings — CE marking affixed wrongly or absent, no EU declaration of conformity or one drawn up incorrectly, registration and documentation failures, no authorised representative. Notice what these have in common: each is checkable in minutes, without any deep technical assessment of the AI itself. Evaluating whether a risk management system genuinely satisfies Article 9 takes expertise and time; checking whether a declaration of conformity exists does not. The widely expected first enforcement wave is therefore procedural — the same pattern the GDPR’s early years followed — which means the companies caught first will not be those with subtle engineering failures. They will be those missing the observable basics.
Which obligations feed this machinery — today and next
The full high-risk walkthrough above becomes routinely available to regulators when the high-risk obligations themselves apply: 2 December 2027 for stand-alone Annex III systems, 2 August 2028 for AI in regulated products. But the machinery is not idle until then — it enforces what is already live: the Article 5 prohibitions and the Article 50 transparency duties, both testable from outside the building, both complaint-triggerable today. And the fine tiers behind it all: up to €35 million or 7% of worldwide turnover for prohibited practices, €15 million or 3% for the Article 99(4) list — which includes Article 50 — and €7.5 million or 1% for misleading authorities, with cooperation a listed mitigating factor and the intentional or negligent character of the breach a listed input. The documentation baseline an authority will ask for first — risk file, technical documentation, declaration of conformity, registration evidence, monitoring plan, logs, quality records, and for non-EU providers the representative’s mandate — cannot be produced in three weeks under pressure. It can be built calmly in the runway that exists right now. That is the entire point of the runway — and building exactly that record, traced to the Official Journal text, is what ExecLevel AI does, in weeks.
Find out what an authority would see if it looked at your systems today — a free assessment conversation at www.execlevelai.eu
Disclaimer: This article is for general informational purposes only and does not constitute legal or compliance advice. EU AI Act requirements may vary depending on your organisation, AI system, and use case. For advice on EU AI Act compliance, visit www.exclevelai.eu